What Is Cybersecurity as a Service for Manufacturers?
What Is Cybersecurity as a Service for Manufacturers?
A plain-English look at ongoing, managed cybersecurity — how it keeps a manufacturer's CMMC posture current between assessments, and what it should cover for shops across Alabama, the Florida Panhandle, and South Georgia.
Overview
Cybersecurity as a Service is ongoing, managed protection — 24/7 monitoring, threat detection, patching, and response — delivered as a subscription rather than a one-time project. Where a risk assessment and a penetration test are snapshots of your security at a point in time, Cybersecurity as a Service is what keeps that posture current every day in between.
For manufacturers under CMMC, that distinction matters more than it might elsewhere. CMMC isn't a one-time badge — it requires an annual self-affirmation that your controls are still in place, and Level 2 requires reassessment on a recurring cycle. A risk assessment shows where you stood on the day it ran; ongoing managed security is what keeps you defensible on every other day of the year, and gives you continuous evidence that your System Security Plan still reflects reality.
Example: A precision parts manufacturer near Montgomery passed its risk assessment in the spring, then had a new, unpatched vulnerability in its remote access software exploited that fall — a gap that ongoing monitoring would have caught and patched within days instead of months.
Benefits
Common Questions
What is Cybersecurity as a Service, and why do manufacturers need it?
Cybersecurity as a Service bundles the ongoing work of protecting a network — monitoring, threat detection, patch management, endpoint protection, and incident response — into a single managed subscription, instead of a manufacturer having to staff and run all of it in-house.
Manufacturers need it because the threat landscape doesn't hold still between annual assessments, and because most shops in the 15-to-100-employee range don't have the staff to run 24/7 security monitoring themselves.
How does it support CMMC compliance?
Several NIST SP 800-171 control families behind CMMC assume ongoing activity, not a one-time setup — continuous monitoring, malicious code protection, timely patching, and audit log review among them. A managed service is how most manufacturers satisfy those controls in practice, since they require daily attention rather than an annual check-in.
It also directly supports the annual self-affirmation CMMC requires — you're attesting that your controls are currently in place, and an ongoing service is what keeps that statement true rather than aspirational.
How is this different from a one-time risk assessment or penetration test?
A risk assessment and a penetration test are both snapshots — thorough, but tied to a specific date. Cybersecurity as a Service is continuous: it's what's watching your network on all 364 other days of the year, catching new threats and misconfigurations as they appear rather than at the next scheduled review.
Example: the assessment might find and fix a dozen existing gaps in March. The managed service is what catches the thirteenth gap that shows up in September, before it becomes an incident.
What's actually included in a Cybersecurity as a Service package?
Typically: 24/7 network and endpoint monitoring, managed firewall and endpoint protection, patch management, email security, security awareness training for staff, log review and retention, and a response process for anything flagged.
Exactly what's bundled varies by provider and tier, so it's worth confirming which of these are included versus billed separately before comparing prices between vendors.
Does it monitor the shop floor, or just office IT?
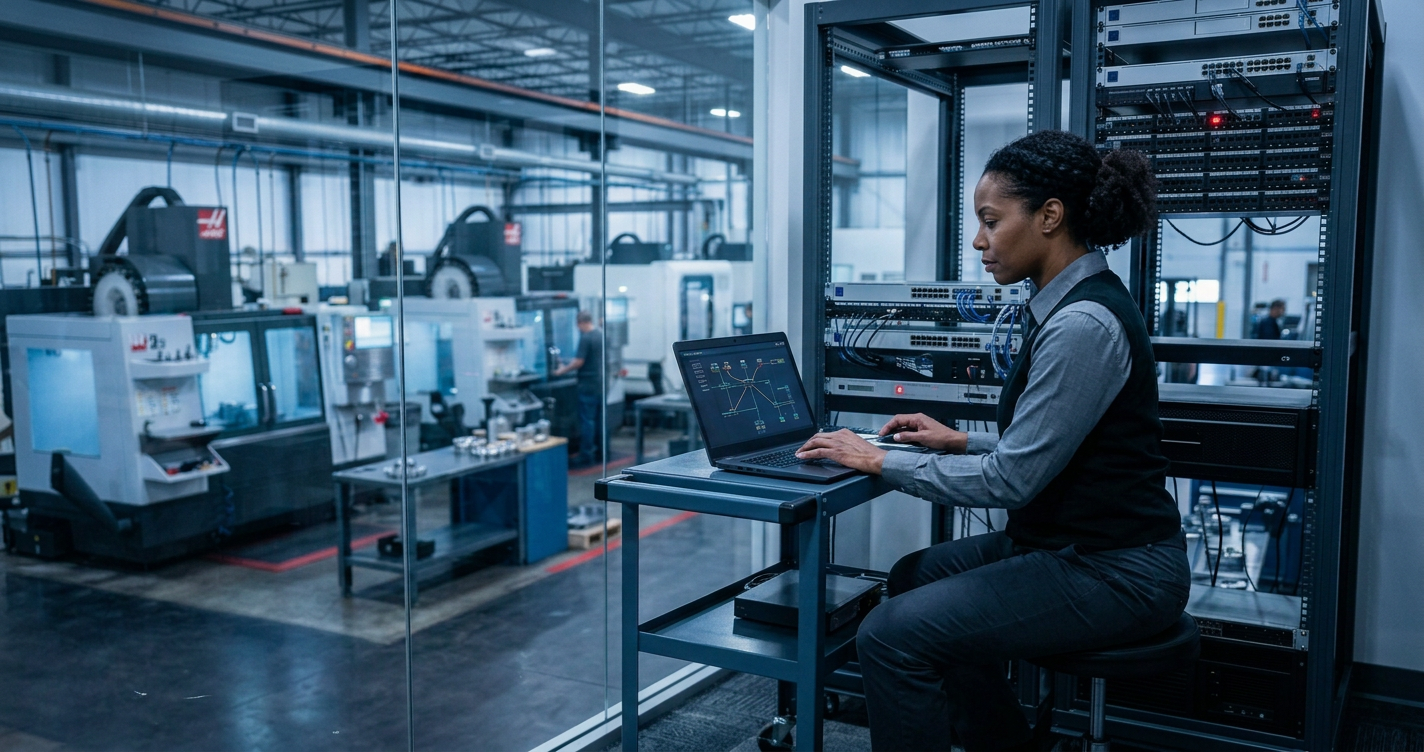
A manufacturing-aware service extends monitoring to the network boundary between office IT and OT — watching for unusual traffic crossing that line, unexpected remote access into machine controllers, and changes to network segmentation — even when it isn't monitoring PLCs or CNC controllers directly the way it would a laptop or server.
Ask specifically what's in scope on the shop-floor side before signing on; generic "IT monitoring" packages often stop at the office network entirely.
How does 24/7 monitoring actually work day to day?
Automated tools continuously watch network traffic, endpoint activity, and logs for anomalies — a login from an unusual location, a spike in outbound traffic, a known-bad file signature. Most of this is automated triage; a human analyst gets involved when something crosses a threshold worth a closer look.
You should get regular reporting on what was caught and handled, not just silence unless something goes badly wrong — that reporting is also part of your ongoing CMMC evidence trail.
How long does it take to get set up?
For a shop in AllTech's typical range — 40 to 75 endpoints, one primary site — onboarding and deploying monitoring agents usually takes one to three weeks, often running in parallel with remediation from a recent risk assessment if one's already been done. Multi-site or more complex OT environments take longer to fully onboard.
How much does Cybersecurity as a Service cost?
It's typically priced per endpoint or per user, per month, which is why cost tracks closely with headcount and device count. It's also normally quoted alongside a shop's broader managed IT spend, since the two are closely related.
Example: for AllTech's typical client — 40 to 75 endpoints — this usually lands within the $4,000-to-$6,000 monthly range for managed IT and security combined, rather than as a large standalone line item.
What happens if we only do point-in-time assessments instead?
Your security posture is only as current as your last assessment date, which means new vulnerabilities, misconfigurations, and phishing campaigns go unnoticed until the next scheduled review — often months later. That's a gap CMMC's continuous-monitoring expectations weren't designed to tolerate.
It's also a harder story to tell a prime contractor: "we checked once a year" is a weaker answer than "here's what our monitoring caught and fixed last quarter."
How does this connect to incident response if something is detected?
Monitoring is what triggers the incident response plan — a flagged event escalates to the containment and reporting steps you've already rehearsed, rather than starting from a cold discovery. The faster the detection, the more of the DFARS 72-hour reporting window you have to work with instead of scramble in.
Ideally the same provider handles both, so detection and response are one continuous process rather than a handoff between two vendors.
How do we choose the right partner for ongoing managed security?
Look for a provider that can speak specifically to CMMC and DFARS requirements, not just generic "managed security" language, and ask exactly what's covered on the OT/shop-floor side versus office IT.
Also confirm they can carry you from assessment through testing through ongoing monitoring through incident response as one connected relationship — switching providers at each stage creates gaps exactly where you can't afford them.
How AllTech Helps
AllTech IT Solutions provides Cybersecurity as a Service for manufacturers across Alabama, the Florida Panhandle, and South Georgia, with monitoring scoped to include the office-to-shop-floor boundary and reporting built to support your CMMC evidence trail. Because we also run risk assessments, penetration testing, and incident response planning, this isn't a handoff between vendors — it's one team carrying your security posture from initial assessment through everyday monitoring to incident response.
Key Areas Addressed
Cybersecurity as a Service
Ongoing 24/7 monitoring, patching, and managed defense for your whole environment.
Learn more →Advanced Cyber Protections
Layered defenses for the higher-risk parts of a manufacturing environment.
Learn more →Cybersecurity Risk Assessment
The starting-point gap analysis that ongoing monitoring keeps current.
Learn more →Network Penetration Testing
Periodic real-world validation that your monitored defenses actually hold up.
Learn more →Incident Response Handbook
The rehearsed plan monitoring escalates into when something is detected.
Learn more →Managed Solutions
Full managed IT support that ongoing security monitoring is typically bundled with.
Learn more →AllTech's Approach, in Short
1. Monitoring extends to the office-to-shop-floor boundary, not just the office network.
2. Regular reporting builds the ongoing evidence trail your CMMC affirmation relies on.
3. Detected issues get patched or escalated, not just logged and left for later.
4. One team carries you from assessment through testing through monitoring through response.
5. Predictable monthly pricing scoped to your endpoint count, not a surprise bill after an incident.
Is anything watching your network between assessments?
AllTech can provide ongoing, CMMC-aware Cybersecurity as a Service scoped to your production environment.
Call 205-290-0215